Cycurion Fathom · The predictive intelligence platform
See the attack before it surfaces.
Fathom is the platform Panoptic and Habit run on. It joins what they see with the tools you already own, scores it in context, and shows which attack is most likely next and what stops it.
Other platforms tell you what happened. Fathom tells you what happens next.
Dive
Every other tool stops at the surface.
Sunlight zone
1,284Alerts in the last 24 hours. The surface: what each tool saw, after it happened, one alert at a time.
Deeper
6 + 4Signals that belong together. Fathom resolves what Panoptic, Habit and your own tools each saw separately to the same 6 assets and 4 identities.
The abyss
1Attack path, most likely to be used next. With the evidence behind it and the fix that cuts it. This far down, only Fathom is looking.
Illustrative data
Command
What is most likely to hit us, and when?
Breach likelihood today, where it is heading if nothing changes, and the reasoning in plain English. Always a probability, never a certainty.
Breach likelihood in the next 30 days, and the projected peak if no action is taken
Why Fathom predicts this
A privileged credential, svc_lab_integration, is for sale on a ransomware-affiliated forum and has no MFA. It can reach ehr-app-03, which carries a validated Log4Shell entry point, and the SIEM already sees lateral-movement probes toward the domain controller. Rotating the credential with MFA, patching Log4Shell and upgrading the SSL-VPN cut the 30-day breach likelihood from 34% to an estimated 12%, and the projected peak from 74% to 32%.
No single tool flags this. Correlated across
Inside Cycurion Fathom
Every screen answers one question.
01 · Attacker positioningWhere is the attacker positioning?
A live map of your assets and the predicted path through them, from the internet edge to the data that matters.
VPN credential to clinical app to DC to PHI store
- InternetPositioning
- vpn-gw-02Edge
- ehr-app-03Clinical app
- dc-core-01Domain controller
- ehr-db-01Objective, PHI
02 · Predicted attack traceHow would the attack unfold?
The modeled sequence, step by step in elapsed time, mapped to MITRE ATT&CK. Every step carries the one action that breaks it.
T+00:00Initial accessExposed svc_lab_integration credential used on the vpn-gw-02 SSL-VPN
T1078 · Valid Accounts× Break here: Rotate credential + MFAT+00:12FootholdLog4Shell triggered on internet-facing ehr-app-03
T1190 · Exploit Public-Facing App× Break here: Patch Log4ShellT+01:04Credential harvestingLSASS access on ehr-app-03; cached domain credentials recovered
T1003 · OS Credential Dumping× Break here: EDR isolate hostT+02:20Lateral movementKerberos to dc-core-01 via the clinical app-tier trust
T1550 · Use Alt Auth Material× Break here: Segment EHR tierT+04:10Domain compromiseDomain admin obtained on dc-core-01
T1078.002 · Domain Accounts× Break here: Tier-0 isolation + JITT+06:45Data stagingehr-db-01 patient records enumerated and staged
T1074 · Data Staged× Break here: DLP + DB egress lockT+09:30Ransomware detonation + exfilEncryption begins, care delivery disrupted, HIPAA breach notification
T1486 · Data Encrypted for ImpactImpact: prevent before this step
03 · Break the attackWhat do we do first?
The top preventive actions, ranked by how much each one cuts the projected peak, and the combined effect of doing all three.
ActionCut to peak
- Rotate the 3 exposed credentials + enforce MFA on svc_lab_integration−16%Identity · buys ~6 days
- Patch Log4Shell (CVE-2021-44228) on ehr-app-03−15%Vulnerabilities · buys ~5 days
- Upgrade FortiOS 7.2.5 to 7.2.7 on vpn-gw-02−11%Vulnerabilities · buys ~4 days
Apply these 3
- Next 30 days34% → 12%
- Projected peak74% → 32%
04 · Breach simulatorWhat if we fix these three?
Toggle preventive actions and watch the modeled peak likelihood recompute, before anyone touches production. Send the plan to remediation when it looks right.
- Rotate credentials + MFA−16%
- Patch Log4Shell on ehr-app-03−15%
- Upgrade FortiOS on vpn-gw-02−11%
- Segment the EHR tier−8%
- Tier-0 isolation + JIT admin−7%
Next 30 days: 34% → 12%
Predicted path
- vpn-gw-02 · Entry pointcut
- ehr-app-03 · Footholdcut
- dc-core-01 · Escalationopen
- ehr-db-01 · PHI objectiveopen
05 · ValidationIs this finding really exploitable?
Offensive agents test whether findings are exploitable inside your network, safely and continuously, and show what your existing controls already block.
- Log4Shell exploit chain, clinical app tierExploitableehr-app-03 (replica) · CVE-2021-44228
- EternalBlue precondition, file serverExploitablefile-svr-04 · CVE-2017-0144
- Perimeter sweep, patient portalBlockedweb-portal-01 · multiple
How it works
Telemetry in. Foresight out.
Panoptic feeds it exposure, Habit feeds it behavior, and the tools you already own add breadth. Four layers turn it into one prediction.
01 · Data in
02 · The Fathom engine
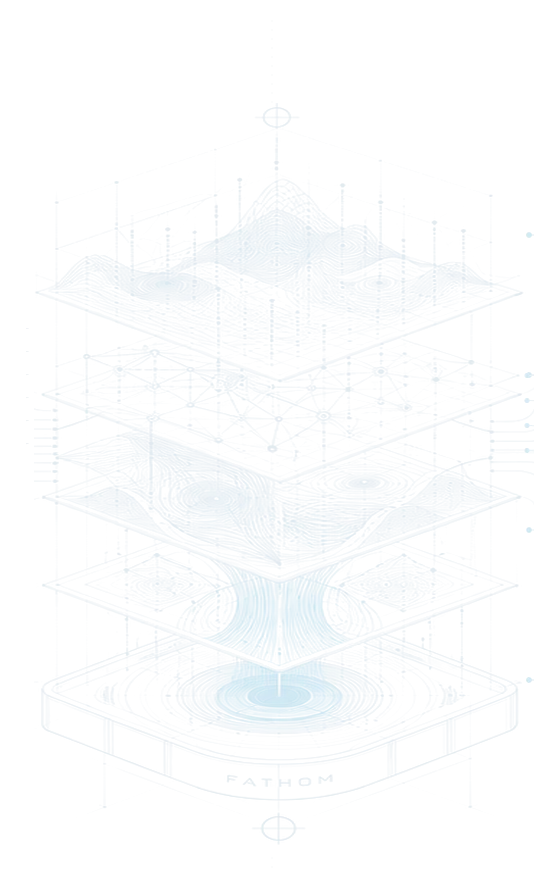
- CorrelateResolve shared identities and link related signals.
- DetectRecognize emerging patterns and separate noise from signal.
- PredictModel probable attack paths and estimate likely impact.
- SimulateTest intervention scenarios and compare expected outcomes.
03 · What you get
Better together
One instrument gives you a reading. Several give you a forecast.
Neither module was wrong. Neither was enough.
Integrations
Keep the tools you own. Fathom makes them talk.
- EndpointCrowdStrike, Microsoft Defender and other endpoint agents
- IdentityMicrosoft 365, Google Workspace
- Email and domainsMail flow, DNS records, domain spoofing reports
- NetworkFirewalls, routers and the ISP edge
- Cloud and SaaSCloud workloads and the applications your teams run
- Exploit intelCISA KEV, FIRST EPSS, MITRE ATT&CK
Connected through API. Ask us about yours.
The abyssal plain · 2,200 fathoms
Alerts are noise. Intelligence is Cycurion.
Book a demo and watch Fathom take signals from Panoptic, Habit and the tools you already run, and turn them into one prediction you can act on.
Book a demo